When AI Goes Agentic, Governance Has to Get More Granular
Agentic AI is changing AI governance in financial services, requiring institutions to define permissions, human authority and controls at the level of individual actions and workflows.
The Bright Recap
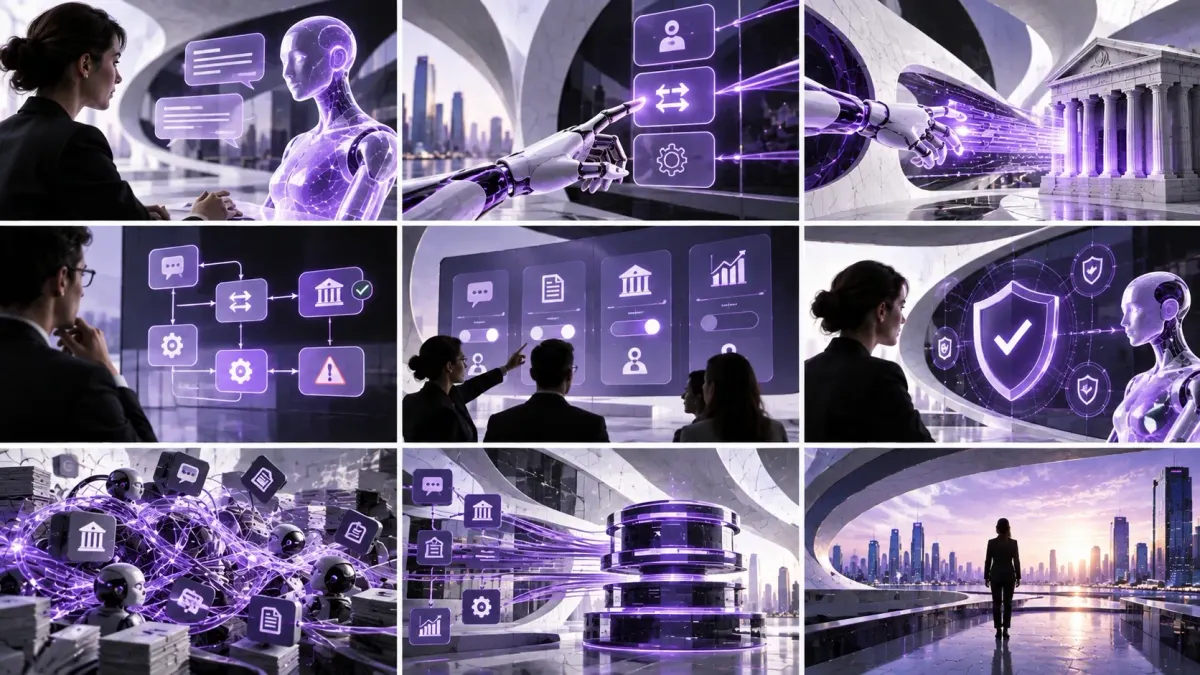
Agentic AI is changing the governance challenge for financial institutions: instead of governing only what AI produces, organizations increasingly need to govern what AI is authorized to do. That means setting permissions and controls at the level of individual actions, workflows and use cases.
To know more about this topic, read our related articles:
- The Deterministic Advantage Fintechs Already Own
- Agentic AI as a Catalyst for Intelligence and Resilience in Fintech Ecosystem
- Mastercard Q1 2026: The Earnings Call That Put AI Spending on Your Behalf at the Center of Global Payments
- Financial technology explained
- Cantica Business Reports
Bright Answers
What changes when AI becomes agentic?
Governance shifts from primarily overseeing what AI produces to governing the actions AI can take within financial workflows.
Why should financial institutions govern AI at the use-case level?
Different AI interactions can carry very different risks, even when they use the same AI system. Governance therefore needs to reflect the specific data, permissions and authority required for each task.
Does agentic AI eliminate the need for human oversight?
No. The article argues that institutions should determine where human authority belongs within each workflow, including when AI can retrieve information, recommend, initiate or execute an action, and when human approval or escalation is required.
For most of the generative AI era, financial services businesses have been governing something AI produces: an answer, a summary, a recommendation, a piece of content. This is largely a matter of vendor governance — ensuring the AI models themselves are secure, reliable, and compliant.
Agentic AI changes the object of governance. Now we increasingly have to govern actions.
AI agents will go from telling a customer how to make a payment to actually initiating that payment on their behalf. Agents will move from summarizing an account history for an employee to determining the next step in a workflow — and executing it. And in some cases, agents won't be waiting for someone to ask a question at all — they'll be identifying needs and initiating interactions all on their own.
Meet Cantica, the Fin-Tech intelligence system for custom reports to strategise your next business move.
That progression from AI that answers to AI that acts requires that financial institutions develop a new kind of operational AI governance, centered on a harder question: how much authority should an AI system have once it is connected to the actual operations of a financial institution?
There is no universal answer to that question. Effective operational AI governance requires institutions to make that decision at a much more granular level: action by action, workflow by workflow and use case by use case.
Three principles can help:
1. Govern the use case, not “AI.”
It’s tempting to create broad institutional rules: AI can access this type of information but never that type. AI can perform this action but never that one. Customer-facing AI requires one set of controls; internal AI requires another.
The problem is that these categories quickly become too broad to be useful. Consider two interactions handled by the same customer service AI: A customer asks for the address of the nearest branch; another wants to initiate a wire transfer.
Technically, both are customer service interactions — and both may be handled by the same customer-facing AI agent. Yet, operationally, they have almost nothing in common. The consequences of an error, regulatory requirements, data involved and appropriate level of AI authority are radically different.
That’s why operational AI governance should follow the familiar security principle of least privilege. Start with an inventory of the specific interactions and workflows in which AI participates. Determine the risk profile of each. Then give AI only the data access, permissions and authority required to complete that particular task.
The same thinking applies internally. An AI summarizing a customer's interaction history for an employee doesn't require the same authority as an agent taking action on the customer's account. An AI helping collect information for a loan application isn't equivalent to one participating in an underwriting decision.
In short, as AI capabilities expand, the question “What should our AI be allowed to do?” is replaced by “What should it be allowed to do here?”
2. Stop talking about the "human in the loop.”
One of the most common phrases in AI governance is also becoming one of the least precise: human in the loop. It suggests that the two possible governance models are AI acting independently, or with a person supervising.
Real financial workflows are much more complicated. In one workflow, an employee might retain complete decision-making authority while AI retrieves information, summarizes history and recommends a next step. In another, AI could autonomously complete most of a process but require human approval before one consequential action. And in yet another, AI could execute an entire low-risk, highly repeatable interaction while escalating only exceptions.
The overarching governance question, then, is: Where does human authority belongs within the workflow? Where can AI retrieve information? Where can it recommend an action? Where can it initiate one? Where can it execute? Which decisions require approval? What circumstances trigger escalation?
As agentic AI becomes more capable, those questions only grow more consequential — and the answers more nuanced. Instead of the binary of “human in the loop” or not, organizations need to ensure the right human is involved at the right moment for the right reason.
3. Fewer AI brains mean fewer authorities to reconcile.
Like every other tech wave before it, the first wave of enterprise AI adoption left most financial institutions with a fragmented AI stack. Individual departments bought copilots, teams deployed specialized chatbots, business units tested models and agents designed for specific tasks.
But now, as institutions prioritize AI governance, they're dealing with dozens of systems — with their own permissions, integrations, data access rules, policies and controls. Some organizations are responding by adding separate governance technologies above their existing tools — another layer to a growing cake.
The classic tech consolidation exercise can likely deliver some budgetary and administrative efficiencies. But effective AI consolidation will immediately deliver governance value: Fewer AI “brains” mean fewer permissions to define, fewer policies to reconcile and fewer autonomous actors whose authority must be understood.
Financial institutions should regularly inventory their AI environments and ask where capabilities can be consolidated. Can several workflows run through a common platform? Can permissions and policies be centrally administered? Can a smaller number of vendors support a broader range of AI applications?
Governance has to follow the action
Financial services businesses already understand the importance of authority. Employees have roles, permissions, transaction limits, approval requirements and escalation paths. High-risk actions receive greater scrutiny than routine ones.
Agentic AI needs to get that same granular scrutiny. As AI begins participating more actively in financial workflows, institutions need to bring that same precision to governing machines, defining exactly what it is authorized to do in each situation.
That requires a different way of thinking about governance: you're not just governing the model — you're governing the action.
Editor's note
Every piece published on The Bright Minded goes through careful verification, but mistakes can happen. If you spot an error, have additional information, or want to flag anything, write to rosalia@thebrightminded.com.